Indian Hackers Used Anthropic's Claude To Breach OpenAI Systems, Earned ₹6.27 Lakh Bounty
· Free Press Journal
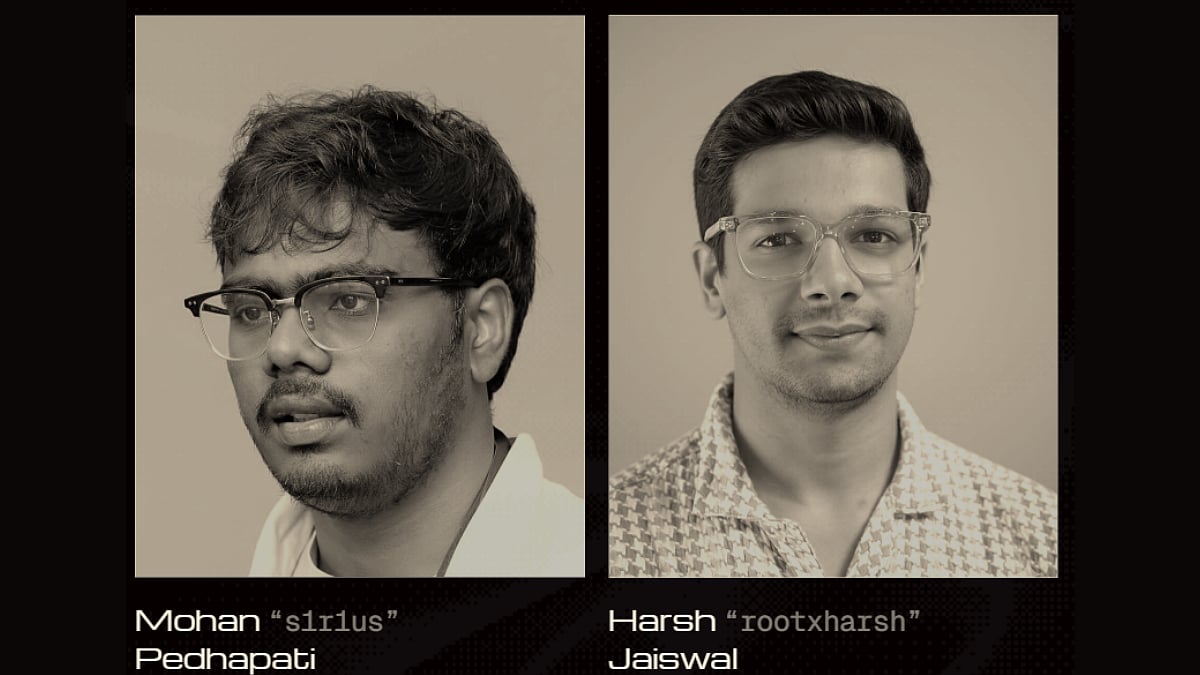
A team of three Indian security researchers used Anthropic's Claude AI models to chain together two software flaws and break into OpenAI's internal systems, ultimately gaining access to employee ChatGPT accounts and the company's internal GitHub code repository.
The researchers and the exploit
Visit casino-promo.biz for more information.
According to WSJ, researchers Harsh Jaiswal, Mohan Pedhapati, and Rahul Maini spent under $3,000 on AI tokens to combine a heap overflow bug in OpenAI's image decoder with a sign-on vulnerability. The chained exploit gave them access to ChatGPT accounts belonging to OpenAI employees, as well as the company's internal "openai/openai" code repository.
At a high level, this was the full exploit chain.
— s1r1us (@S1r1u5_) September 18, 2026
1. HEIC/HEIF upload
2. ImageMagick decoding
3. Heap overflow on libheif
4. RCE on https://t.co/uiccfqfPbX
5. Critical OpenAI SSO flaw
6. ChatGPT/Codex takeover
7. Connected GitHub access
8. Internal repo PR… pic.twitter.com/nr2jEvKXT3
Proof of access, not exploitation
Rather than exploring the internal systems they had broken into, the researchers say they used the compromised access responsibly. They had an employee's connected coding assistant, Codex, open a pull request, inside OpenAI's internal repository purely to demonstrate that the access was real, before disclosing the vulnerabilities to OpenAI.
The report states that the disclosure earned the team a $6,500 (roughly Rs. 6.27 lakh) bounty from OpenAI, though it noted that testing against the community forum used in the initial stage of the attack fell outside the official scope of OpenAI's bug bounty programme.
We reported the bug to Discourse and OpenAI. OpenAI fixed the SSO issue roughly 14 hours after our initial submission.
— s1r1us (@S1r1u5_) September 18, 2026
Discourse received our separate report Saturday, replied Sunday, and had a fix Monday.
OpenAI awarded us $6,500. pic.twitter.com/WeSzRtf14N
AI as an attack accelerant
The case, per WSJ, underscores AI's growing role in cybersecurity offence, with one company's model effectively used to penetration-test a rival AI lab at a fraction of the cost and time such an operation would traditionally require. The report noted that the incident is fuelling calls for stronger safeguards across AI companies as models grow more capable of autonomously finding and weaponising software vulnerabilities.